6 ChatGPT prompts to help improve your business’s cyber security
Cyber security can feel like another responsibility on an already busy list. You know it matters, but turning that concern into clear actions is often the difficult part. This is where ChatGPT can be useful. It can help you draft checklists, explain unfamiliar terms and prepare training exercises that make security easier to discuss with your team. The value comes from what you do with those drafts. A checklist needs someone to check it. A plan needs an owner. A training exercise needs a conversation afterwards.
Below are six prompts you can adapt, with fictional examples and a practical next step for each.
Before you start: protect what you put into a prompt
Use fictional examples or a general description of your business. Keep passwords, recovery codes, customer records, confidential documents and detailed security configurations out of prompts. Removing names alone may leave information that identifies a person or exposes your business.
Before using AI at work, check which tools your organisation allows and what information you’re permitted to share. The UK’s National Cyber Security Centre (NCSC) advises taking care with sensitive information when using tools such as ChatGPT. Read its guidance on ChatGPT and large language models (LLMs).
Treat generated answers as drafts. ChatGPT can make mistakes and cannot confirm your systems’ security based on a description. Check technical recommendations against current official guidance and ask your IT provider to review changes that affect live systems.
1. Turn a vague concern into a practical improvement plan
“We need better cyber security” is difficult to act on. “Check how staff sign in to email and appoint someone to review access” gives you somewhere to start.
The NCSC’s small organisation guidance covers protecting email, accounts and devices, backing up data and spotting attacks. These are useful starting points for a review. Explore the NCSC guide.
Example: The draft might suggest checking whether all email users have multi-factor authentication, an additional step or factor used to confirm identity when signing in.
Put it into practice: Ask your account administrator to verify the actual settings. Record what is enabled, what remains outstanding and who will address it.
2. Create a short phishing awareness exercise
Phishing is an attempt to trick someone into revealing information or taking an unsafe action, often through a message that appears trustworthy. A familiar scenario can make a team discussion more useful than a long presentation. Read the NCSC guide on spotting cyber attacks here.
Example: A fictional supplier asks for an urgent payment to a new bank account. The discussion should focus on verifying the change through a trusted contact method already held by the business.
Put it into practice: Run the exercise openly in a team meeting and agree how suspicious messages should be reported. Do not rely on ChatGPT to declare a real email safe.
3. Build an account access and leaver checklist
When someone changes role or leaves, their access needs attention. It’s always best to review access to important accounts and remove or disable accounts that are no longer needed. It is also recommended passkeys where available, with strong unique passwords and two-step verification where passwords remain in use.
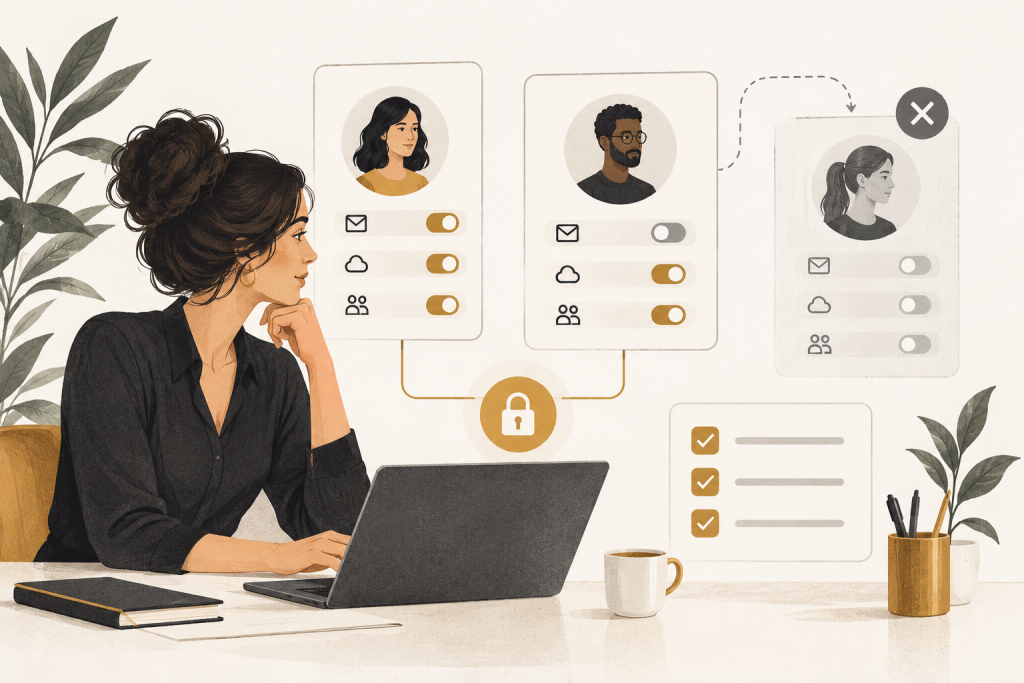
Example: A departing contractor may have transferred their files but still retain access to the website or social accounts.
Put it into practice: Have each system owner confirm completion. Check retention requirements and ownership before deleting anything, and avoid removing the business’s only administrator.
4. Prepare a backup recovery test
It is recommended to make copies of the data your business needs to operate. A useful follow-up question is whether you can restore the right data when you need it.
Example: Your test could restore a sample folder to a separate location and check that the files open correctly.
Put it into practice: Agree the method with your IT provider, perform the test and record the result. A generated plan does not prove that a backup works.
5. Rehearse what happens during a cyber incident
An incident response exercise lets people practise decisions before an emergency. The NCSC’s response and recovery guidance covers preparation, identifying what is happening, resolving the incident, communicating and learning afterwards.
Example: Your discussion may reveal that the IT provider’s contact details are only stored in the email account you can no longer access.
Put it into practice: Keep an approved response plan and contact list accessible during an outage. During a real incident, follow that plan and contact your IT or security provider promptly.
6. Draft clear rules for using AI at work
Using AI to support security also means thinking about how staff use AI. A short, specific policy gives people clearer choices than a vague instruction to “be careful”.
Example:Drafting a training exercise with invented details could be permitted. Uploading a customer spreadsheet to an unapproved tool should be prohibited.
Put it into practice: Have the relevant business, IT and privacy owners review the draft. Confirm the actual approved tools and rules before sharing it with staff.
Make one improvement this week
Choose the prompt that addresses your biggest unanswered question. Review the draft, assign an owner and agree what evidence will show the action is complete.
The useful outcome is a checked account setting, a completed recovery test or a team that knows how to report a suspicious message. ChatGPT can help you prepare the work. People still need to carry it through.


You May Also Like
What is Product Discovery? A Friendly Dive into the World of Innovation
Understanding OKRs: A Simple Guide with Everyday Examples